•
AI
•
Security
October 19, 2026
How to evaluate an AI financial assistant before you give it your business data
These days, connecting an AI financial assistant to your business can take one click: open the app’s integration screen, pick QuickBooks or your payment platform, and click Allow. From that moment on, the assistant can read, and maybe even change, everything that connection reaches, from customer balances to saved payment methods to invoices.
Business owners know that this one click carries significant risk. When Bluevine surveyed 942 U.S. small business owners and financial decision-makers in April 2026, data security and privacy topped their list of roadblocks to AI technology adoption, named by 33% (up from 23% in 2025). That concern is reasonable, but it doesn’t have to stall you. Start with a clear set of questions to ask before you connect to any AI financial assistant, plus the proof each answer should come with.
This guide gives you 12 questions to ask any vendor before you click Allow. Each question comes with the evidence to request and the red flag that should stop the deal. You'll also get a 20-minute demo test to run with your own login.
What changes when an artificial intelligence (AI) assistant connects to your financial data?
An AI financial assistant uses artificial intelligence to answer questions and offer insights about your finances in plain English. Some tools can also take action, like sending invoices or charging credit cards. For the basics, start with our guide to what an AI finance assistant is.
An AI assistant works at 3 access levels, and the last one raises the stakes.
Level 1: You paste data in
You copy a budget or an expense report from large spreadsheets, Excel, or Google Sheets into a chat with a generative AI tool. It sees only what you share, but that information now sits with a third party. Our comparison of ChatGPT for accounting and connected financial intelligence covers the trade-offs.
Level 2: The AI reads your systems live
The assistant connects to data sources like your accounting system, PSA (professional services automation) tool, or payment platform and can combine live data from connected systems before answering natural language questions in real time. It can pull financial statements, analyze spending, sort expenses into categories, or run cash flow forecasts with full context on your accounts; some tools also use alerts to flag unusual spending or overspending and improve transaction transparency. Budget apps and banks have offered spending insights based on your transaction patterns for years, but a connected assistant can see far more than you'd ever paste into a chat.
Level 3: The AI takes action
It creates invoices, charges cards, pulls ACH payments (electronic transfers between banks), or issues refunds, and some assistants can also handle repetitive payment actions once they are allowed to act. At this level, a mistake has real consequences. A wrong charge or unapproved refund costs you time to fix and your client’s trust.
The closer it gets to your money, the more you need to know before you connect. But many organizations still haven’t put basic guardrails in place; IBM’s 2026 Cost of a Data Breach report found that only 40% of organizations use access controls on AI models and data. Here’s a quick comparison of what each level puts at risk.
| Level | What the assistant can do | What's at risk |
|---|---|---|
| Paste | Sees only what you share in a chat | Data shared outside your systems |
| Read | Reads accounts, invoices, and transactions in real time | Client and payment data exposure |
| Act | Creates invoices, charges cards, and issues refunds | Client trust or your reputation if a mistake or fraud sends a charge or refund to the wrong place |
Ask the vendors behind AI tools for evidence, not reassurance
Every AI vendor will talk up how secure their product is. Protect yourself by asking for the following types of evidence:
- Paper: the contract, data terms, or audit reports, such as the clause that says whether your data trains their model
- Product: the setting or screen that enforces the answer, such as role permissions that stop a limited user from issuing refunds
- Proof: watching it happen in a demo, signed in with your own role, such as asking for an action your role can't take and seeing it refused
Then score each answer as documented, shown live, or "we'll get back to you." Treat the last one as a no until it changes.
Confidence isn't evidence. In Okta's AI Agents at Work 2026 research, 95% of executives said they're confident their company could detect AI acting outside its intended scope. Yet only 34% of organizations hold their AI agents to the same security controls they use for their employees.
In other words, businesses feel more protected than their safeguards actually make them, so ask vendors to show you the controls behind their claims.
Permissions: what can it see, and what can it do?
Since every other answer depends on access, permissions are a good place to start. A Cloud Security Alliance study conducted in 2025 found that 53% of organizations had AI agents exceed their intended permissions.
To keep that from happening to you, these 4 questions show you how far an assistant’s access goes before you connect.
| # | Question | Evidence to ask for | Red flag |
|---|---|---|---|
| 1 | What data can it read, and from which systems? | A list of connected systems, such as your PSA (ConnectWise, Autotask, HaloPSA, or SuperOps) and accounting tools (QuickBooks or Xero), and the access each connection grants | It asks for access it doesn't need, such as write access to your bank |
| 2 | Does it follow the user roles we already have? | Role documentation, and a demo signed in as a limited user | One admin connection that gives every user the same power |
| 3 | Can it see other customers' data, or can they see ours? | A security overview and the scope of the SOC 2 report | Vague talk of "shared learning" across customers |
| 4 | Which actions can it take, and who can trigger each one? | A list of actions by role | No list, or any user can trigger any action |
Why should an AI-powered assistant follow your existing roles?
Your team already has roles in your PSA and accounting system. In theory, a good AI assistant inherits them, so you stay in control, like a technician who can’t issue credits in your PSA and therefore can’t issue them through a chat either.
Vendors love to promise an easy integration experience, but it’s just as important to understand what the AI can read and write before you connect it. Here are a few hypothetical examples of what happens when users get access they shouldn’t have:
- An MSP’s helpdesk technician can pull up every client’s saved payment method, even though they don’t need card or bank details to close tickets.
- An agency account manager accidentally sends milestone invoices before the client signs off, so now your team has to issue credits and explain the mistake.
- A sales rep at a reseller asks for a refund to settle a complaint, and the assistant issues it before a manager can review it.
In each case, the assistant did exactly what the connection allowed. That's why question 2 (“Does it follow the user roles we already have?”) matters so much. Ask the vendor to sign in as a limited user during the demo and show you what changes. Permissions should also define which routine tasks each role can trigger through the assistant.
Data use: where does your data go after it's read?
What a vendor does with your business data comes down to what’s written in the contract, not what they say in a demo. Find out by asking these questions about data use, security, and compliance disclosures in the contract:
| # | Question | Evidence to ask for | Red flag |
|---|---|---|---|
| 5 | Is our data used to train or improve AI models? | A clause in the contract or data terms, with an opt-out if training happens | "We may use data to improve our services," and nothing more |
| 6 | Which AI models and subprocessors touch our data, and where is it stored? | A subprocessor list, the hosting location, and notice before changes | They can't name the model provider or where data is hosted |
| 7 | How long do you keep our questions, answers, and synced data, and what happens when we leave? | A retention policy and a deletion commitment at contract end | Indefinite retention, or deletion only on request with no deadline |
| 8 | Who has independently tested your security? | A current SOC 2 Type II report (often under NDA), plus proof of PCI-DSS (Payment Card Industry Data Security Standard) compliance if it handles card data | "We're working towards SOC 2" with no date, or a self-assessment only |
Questions 5 and 6 deserve extra attention. Many generative AI tools improve their models with usage data, which can include your clients’ names, balances, and payment history. They may also send your questions to an outside model provider. Get the following in writing:
- What “improve” means
- Who processes your financial data
- Whether you’ll hear about future model, storage, or subprocessor changes first, and any related disclosures
- How to opt out of model training
As for question 8, know the difference between the two types of SOC 2 (System and Organization Controls 2) reports. A licensed auditor issues both, but a Type I report checks whether a vendor’s security controls are designed properly at a single point in time, while a Type II report tests whether those controls actually worked over an observation period of 3 to 12 months.
And if the AI assistant can charge cards or access card data, ask for proof of PCI-DSS compliance.
Approvals: what happens before it changes anything?
Once an AI assistant can move money, the risk changes, and the most helpful approval flows show exactly what will happen before any change is made. Closely examine what it shows you before it acts, and what happens when you say no, by asking the following questions:
| # | Question | Evidence to ask for | Red flag |
|---|---|---|---|
| 9 | What does it show us before it acts? | A live confirmation naming the exact change: customer, amount, invoice | A generic "Approve changes?" prompt, or one click that approves many actions at once |
| 10 | What happens if nobody approves, or we say no? | The confirmation expires, and a declined action isn't retried | The action runs anyway after a timeout |
| 11 | Can we see afterward who approved what? | An activity log with the action, the approver, and the time | No log, or one only support can pull |
| 12 | How do we pause it or cut off its access? | The setting or contract term that disconnects it, and how fast it takes effect | It takes a support ticket and days to switch off |
A good confirmation does 4 things:
- Names the exact change (including the client, amount, and invoice)
- Asks for one change at a time
- Expires if nobody responds
- Gets logged with who approved it
A generic "Approve changes?" pop-up fails all four. To decide who on your team should approve what, see our guide to keeping a human in the loop with AI agents in finance.
Here’s what that looks like in practice: Alti, the financial intelligence inside Alternative Payments, shows a confirmation card that spells out the exact action in plain language and counts down. When time runs out, the buttons switch off, and nothing happens.
What about automations that run on their own?
Saved automations work a little differently. When you approve and save an Auto-Pay rule or invoice reminder, it runs on schedule without asking you each time. That’s by design, and it’s not the same as the red flag in question 10. Ask who can create or pause those rules and whether each run gets logged. This approval model is ideal when businesses want automation to keep running without giving every user broad action rights.
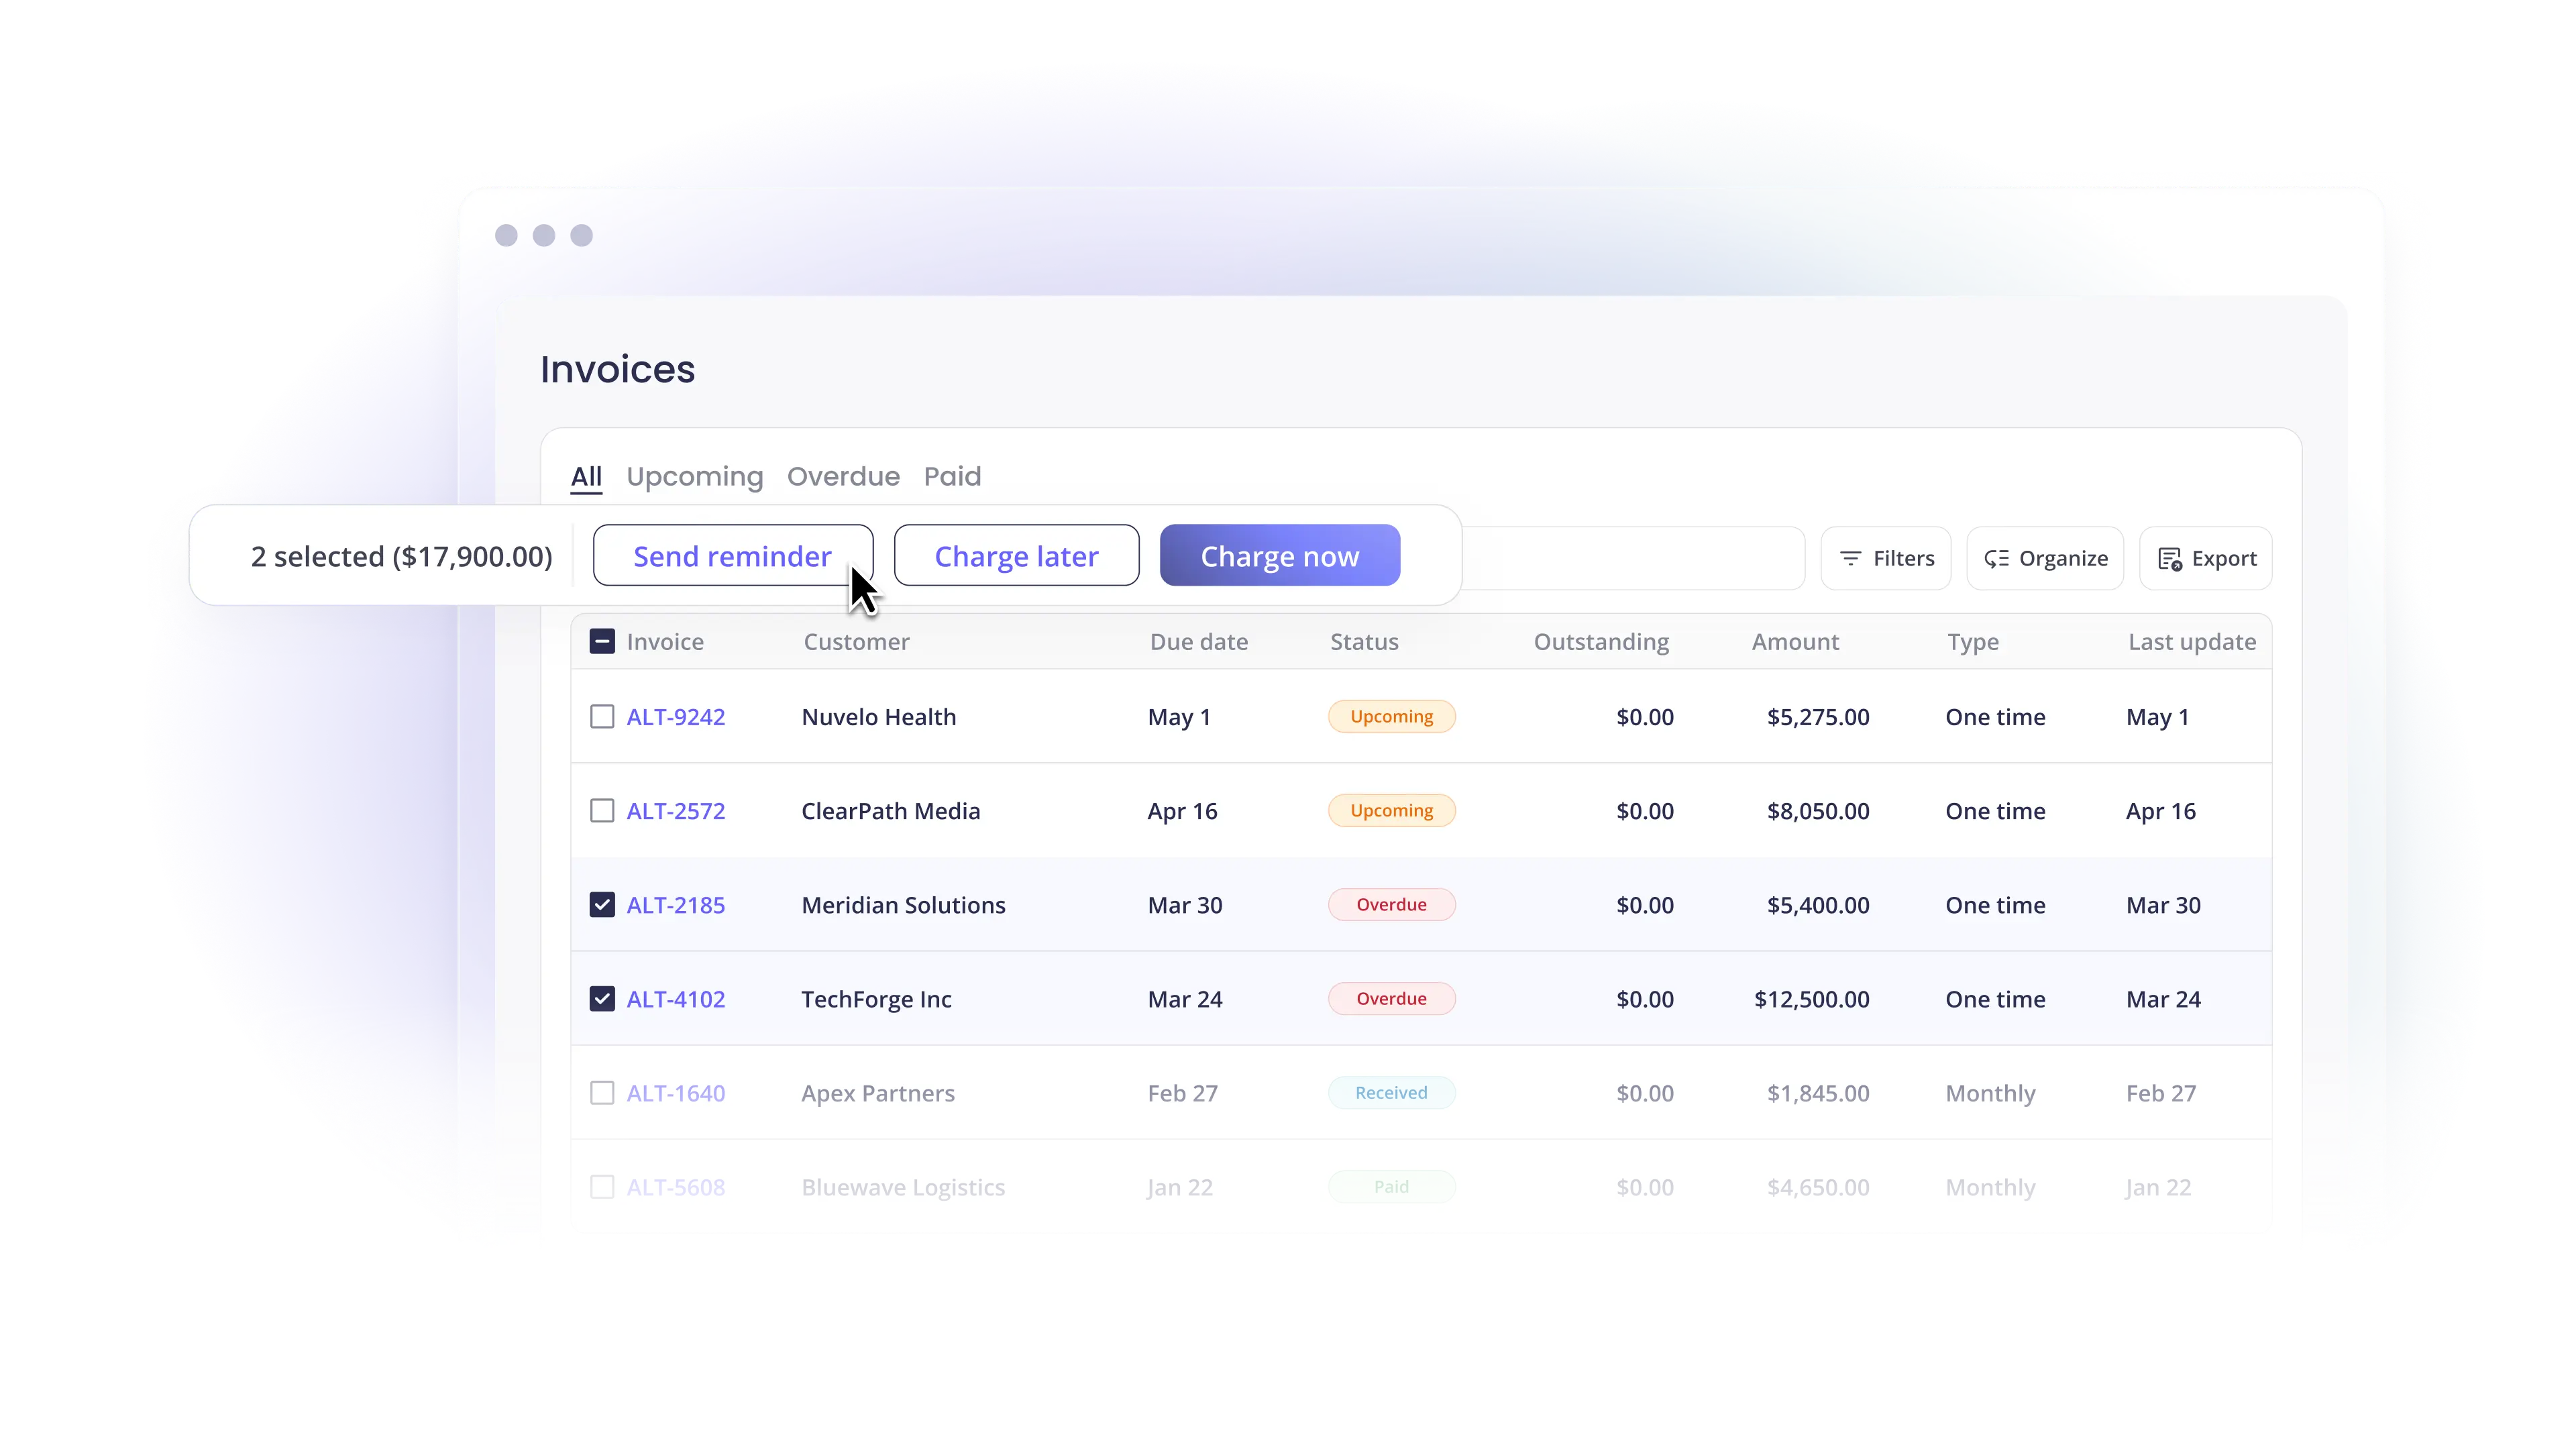
In Alti, only Administrators and Sub-Admins can set up Auto-Pay rules in Accounts Receivable, where automation can shorten the time it takes to get paid.
How to run a 20-minute demo test on any financial assistant
A scripted demo shows you the best-case scenario. This test shows you how the technology behaves when you push past what it’s allowed to do. Bring it to any vendor conversation, and run it yourself.
1. Sign in as your most limited role
In the app, ask for something users in that role can't do, like a refund. Success is a refusal that tells you why.
2. Ask about a company that isn't yours
It should say it can't see that data.
3. Request one real action, like a draft invoice
Read the confirmation before you approve it. Does it show exactly what will change?
4. Decline it
Check that nothing happened and that the assistant doesn't try again on its own.
5. Open the activity log
Find the action, who approved it, and when.
Make sure you ask at least one question you already know the answer to, like your largest overdue balance, and check it against QuickBooks, your PSA, or an Excel export. Even an assistant with perfect permissions can get complex analysis wrong, often because of sync gaps between systems (our guide to ConnectWise QuickBooks integration explains why).
If the results don’t match, ask where its answer came from and what it does when data is missing or out of sync. It’s a red flag if you can't trace a confident answer back to an existing record.
One more piece of advice: send the 12 questions to the vendor before the call, and ask them to fill in the evidence column. What comes back blank tells you a lot.
How Alti, Alternative Payments’ AI-powered financial assistant, answers these questions
Alti is the AI-powered financial intelligence inside Alternative Payments, the platform service businesses use to manage their finances, with core capabilities and features that let you ask questions in everyday language and get live answers from connected Accounts Receivable and Analytics data. In 2025, the AI in personal finance market was valued at $1 billion and is forecast to grow to $3.7 billion by 2033. Here's how it answers the questionnaire, with links so you can check the evidence yourself.
- Permissions (questions 1 to 4): Alti only works with your own account’s data and can’t see any other company’s information. It is designed primarily to work only with your own account’s data and permitted actions. It can only do what your role already allows, so Read-Only users can ask questions but can’t take actions.
- Data use (questions 5 to 8): Alternative Payments is SOC 2 Type 2 certified and PCI-DSS Level 1 compliant. Alti runs inside that same platform, which is built on AWS for financial services data. Model training, model providers, and data retention are covered in the contract review during your demo.
- Approvals (questions 9 to 12): Alti asks you to approve each change before it happens and is built to deliver clear action details before approval, and each confirmed action is logged with who approved it. If you decline, it won’t quietly try again. How to pause access is covered in the contract review.
Bring this list to a demo, and we’ll answer every question on it, demo test included.
Before you click “Allow,” confirm you’ve seen the evidence
An AI financial assistant that deserves access to your business’s finances and your customers’ data can show you the contract terms, the settings that enforce them, and a live test that proves they work. If a vendor can't show this, keep looking.
Alternative Payments is trusted by 1,000+ service businesses nationwide. To see how Alti answers each question, book a demo.
Frequently asked questions (FAQs) about AI adoption and your finances
Is it safe to connect an external or 3rd-party AI financial assistant to my accounting software?
Sort of...maybe...if the assistant limits what it can do and you can verify it. A safe AI financial assistant follows the user roles you already have in accounting tools like QuickBooks or Xero. It asks you to approve each action before any money moves or records change, and it logs who approved what. Ask the vendor for a current SOC 2 (System and Organization Controls 2) Type II report before you connect. It shows an independent auditor tested the vendor’s security controls over several months.
Do generative AI finance assistants train on your data?
It depends. Some generative AI and machine learning products use customer data to improve their models unless the contract says otherwise. Look for a clause in the contract or data terms that says whether your data trains any model, and how to opt out.
What's the difference between read-only and write access?
Read-only access lets an AI financial assistant view data, such as invoices, balances, expenses, transactions, and other numbers, and answer questions about it without changing anything. Write access lets it change that data or act on it, such as creating an invoice, charging a card, or issuing a refund. Write access carries more risk, so it should include role limits, confirmation before each action, an activity log, and clear controls to engage the right approver before each action.
Simplify your customer payments, unlock instant cash flow
Keep reading

How to evaluate an AI financial assistant before you give it your business data
10 questions to ask conversational AI for finance that your dashboard can’t answer